Cybercriminals are scanning servers for the Microsoft Exchange ProxyShell RCE vulnerabilities after technical details presented at the Black Hat

The federal government is pushing hard for agencies to adopt zero-trust cybersecurity architectures, with new guidance released Tuesday from the administration’s policy arm—the Office of Management and Budget—and lead cybersecurity agency—the Cybersecurity and Infrastructure Security Agency. The administration released several documents Tuesday for public comment, seeking feedback on the overarching federal policy from OMB and draft…
The National Security Agency announced Thursday the kick-off of its 20th annual National Cyber Exercise (NCX), a three-day annual cyber competition that tests the offensive and defensive cybersecurity skills of participant teams from U.S. Service Academies and Senior Military Colleges as well as civilian interns from NSA’s cyber-focused development programs. NSA’s National Cyber Exercise (NCX)…
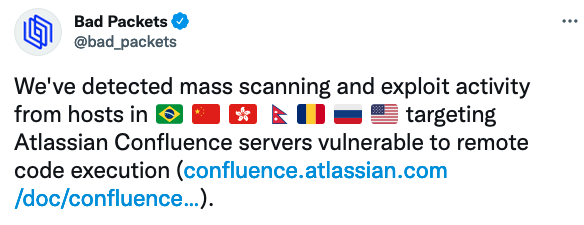
Hackers started exploiting a vulnerability in Atlassian’s Confluence enterprise collaboration product just one week after the availability of a patch was announced. Atlassian informed customers on August 25 that Confluence is affected by a critical vulnerability — described as an OGNL injection issue — that can allow remote attackers to execute arbitrary code on impacted…
The Federal Bureau of Investigation (FBI) and the Cybersecurity and Infrastructure Security Agency (CISA) warn of advanced persistent threat (APT) actors targeting Fortinet FortiOS servers using multiple exploits. In the Joint Cybersecurity Advisory (CSA) published today, the agencies warn admins and users that the state-sponsored hacking groups are “likely” exploiting Fortinet FortiOS vulnerabilities CVE-2018-13379, CVE-2020-12812, and CVE-2019-5591. The attackers are…
Pearson, a London-based publishing and education giant that provides software to schools and universities has agreed to pay $1 million to settle charges that it misled investors about a 2018 data breach resulting in the theft of millions of student records. The U.S. Securities and Exchange Commission announced the settlement on Monday after the agency found…
Breach Notification , Fraud Management & Cybercrime , Identity & Access Management Jim Van Dyke and Al Pascual of Sontiq Describe Criminals’ Use of Breached Data Nick Holland (nickster2407) • March 27, 2021 Jim Van Dyke (left) and Al Pascual of Sontiq Identity crimes are up, but…