CVE-2021-22350
There is a Memory Buffer Improper Operation Limit Vulnerability in Huawei Smartphone. Successful exploitation of this vulnerability may cause the device to crash and restart.
Most mobile app users tend to blindly trust that the apps they download from app stores are safe and secure. But that isn’t always the case. To demonstrate the pitfalls and identify vulnerabilities on a large scale, cybersecurity and machine intelligence company CloudSEK recently provided a platform called BeVigil where individuals can search and check…
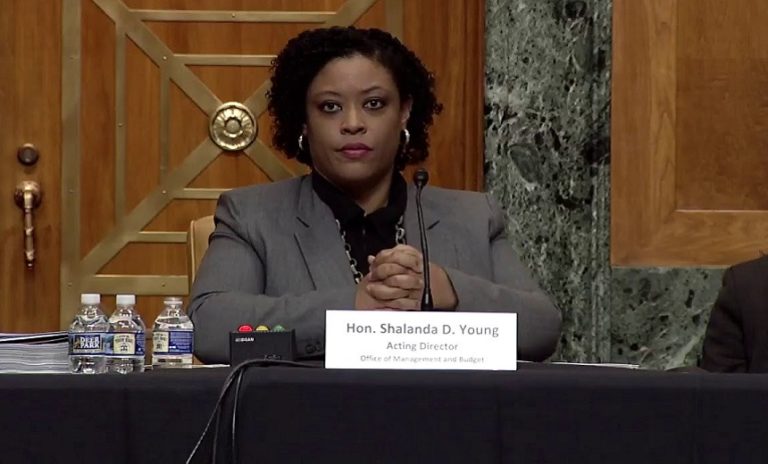
Governance & Risk Management , Government , Incident & Breach Response OMB Memo Describes Steps Agencies Must Take to Report Cyber Incidents Scott Ferguson (Ferguson_Writes) • August 31, 2021 Acting OMB Director Shalanda Young (Photo: U.S. Senate Banking Committee) The White House is ordering U.S. agencies to improve their logging capabilities to better…
Iowa-based farm services provider NEW Cooperative said its systems were offline to contain a cybersecurity incident.The cooperative operates grain storage elevators in the top U.S. corn producing state, buys and sells grain and owns technology platforms for farmers. “We have taken our systems offline to contain the threat, and we…
Executive Summary Informations Name CVE-2021-20292 First vendor Publication 2021-05-28 Vendor Cve Last vendor Modification 2021-05-28 Security-Database Scoring CVSS v3 Cvss vector : N/A Overall CVSS Score NA Base Score NA Environmental Score NA impact SubScore NA Temporal Score NA Exploitabality Sub Score NA Calculate full CVSS 3.0 Vectors scores Security-Database Scoring CVSS v2 Cvss…
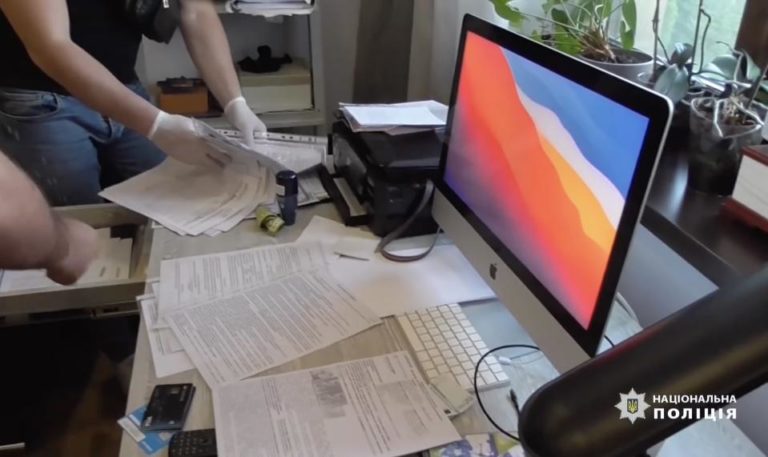
Ukrainian law enforcement officials reported the arrest of the Clop ransomware group on Wednesday. The organization had been disrupting infrastructure and carrying attacks around the world since at least 2019, according to The Hacker News. Six defendants were charged as part of an international operation involving Ukraine’s National Police and authorities from Interpol, Korea,…
# Exploit Title: SAS Environment Manager 2.5 – ‘name’ Stored Cross-Site Scripting (XSS) # Date: 24/06/2021 # Exploit Author: Luqman Hakim Zahari @ Saitamang # Vendor Homepage: https://support.sas.com/en/software/environment-manager-support.html # Version: 2.5 # Tested on: CentOS 7 # CVE : CVE-2021-35475 # Description # SAS® Environment Manager 2.5 allows XSS through the Name field…