The White House Is Deciding Whether to Support a Bureau of Cyber Statistics
The White House Is Deciding Whether to Support a Bureau of Cyber Statistics
Four individuals from Eastern Europe face 20 years in prison for Racketeer Influenced Corrupt Organization (RICO) charges after pleading guilty to running a bulletproof hosting service as a safe haven for cybercrime operations targeting US entities. The bulletproof hosting service was founded by Russian citizens Aleksandr Grichishkin and Andrei Skvortsov, who hired Lithuanian Aleksandr Skorodumov…
Governance & Risk Management , IT Risk Management , Patch Management Patch Tuesday Update: These Vulnerabilities Not Yet Exploited in Wild Doug Olenick (DougOlenick) • May 12, 2021 Microsoft issued patches Tuesday for four more vulnerabilities in on-premises versions of the Exchange Server corporate email platform, one of which is a zero-day flaw….
A man walks near the New York Stock Exchange (NYSE) on August 31, 2020 at Wall Street in New York City.Photo: CFP Chinese ride-hailing giant Didi’s US shares plunged in pre-market trading on Tuesday, in a rout that was joined by two other platform firms that have recently been in China’s cybersecurity crosshairs. As of…
The White House is Deciding Whether to Support a Bureau of Cyber Statistics – Nextgov

Operation Dianxun Overview In a recent report the McAfee Advanced Threat Research (ATR) Strategic Intelligence team disclosed an espionage campaign, targeting telecommunication companies, named Operation Diànxùn. The tactics, techniques and procedures (TTPs) used in the attack are like those observed in earlier campaigns publicly attributed to the threat actors RedDelta and Mustang Panda. Most probably…
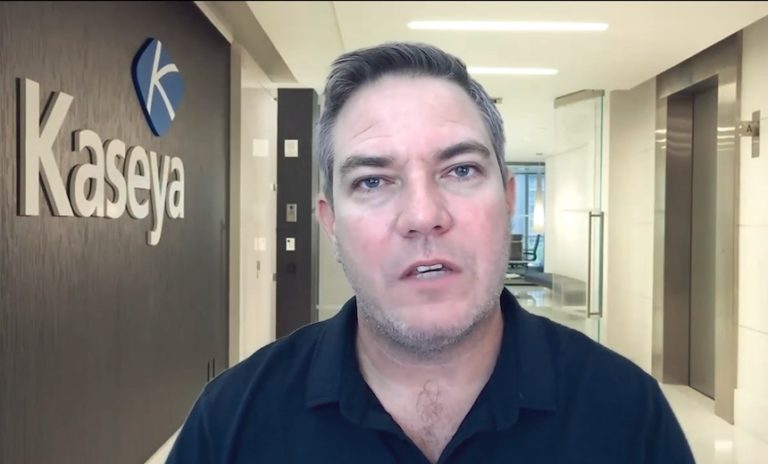
Cybercrime , Endpoint Security , Fraud Management & Cybercrime On-Premises Software Patched, SaaS to Come Online Again Jeremy Kirk (jeremy_kirk) • July 12, 2021 Kaseya Executive Vice President Mike Sanders (Source: Kaseya) Miami-based software company Kaseya released patches on Sunday for its monitoring and management software that was exploited by a ransomware group….