The White House is Deciding Whether to Support a Bureau of Cyber Statistics – Nextgov
The White House is Deciding Whether to Support a Bureau of Cyber Statistics – Nextgov
NVIDIA Windows GPU Display Driver for Windows, all versions, contains a vulnerability in the kernel driver (nvlddmkm.sys) where a NULL pointer dereference may lead to system crash.
Cyberwarfare / Nation-State Attacks , Endpoint Security , Fraud Management & Cybercrime Agency Describes How to Apply Its Cybersecurity Framework Scott Ferguson (Ferguson_Writes) • March 30, 2021 The National Institute of Standards and Technology has drafted guidelines for how to use its cybersecurity framework to address cyberthreats and other security issues that can…
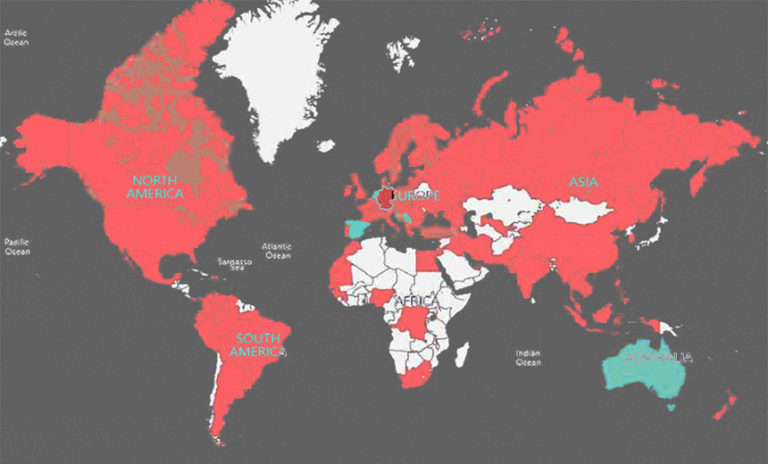
Cybercrime , Cybercrime as-a-service , Endpoint Security Closing EncroChat and Sky, Plus Careful Word-of-Mouth Management, Drove Anom Uptake Mathew J. Schwartz (euroinfosec) • June 18, 2021 The FBI’s map of where Anom users were located as of May (Source: court documents) The global law enforcement “Anom” honeypot operation racked up impressive statistics for…
MSP-focused technology developer Datto Wednesday said it has acquired BitDam, an Israeli developer of cyber threat detection. Tel Aviv, Israel-based BitDam is the developer of the Advanced Threat Protection, or ATP, technology the company claims offers comprehensive defense against malware, … Hi! You’ve reached one of our premium articles available exclusively to subscribers. It’s our…
The federal agency urges organizations to ditch the bad practice and instead use multi-factor authentication methods The Cybersecurity and Infrastructure Security Agency (CISA) has added the use of single-factor authentication to its brief list of bad practices that it considers to be exceptionally risky when it comes to cybersecurity. “Single-factor authentication is a common low-security…
3rd Party Risk Management , Breach Notification , Critical Infrastructure Security Microsoft, FireEye Find Additional Payloads Used During Supply Chain Attack Scott Ferguson (Ferguson_Writes) • March 4, 2021 Researchers with Microsoft and FireEye are disclosing additional malware used by the hacking group that targeted SolarWinds in December 2020, according to a pair of…