Crypto hacker offered reward after $600m heist
Crypto hacker offered reward after $600m heist
Iowa-based farm services provider NEW Cooperative said its systems were offline to contain a cybersecurity incident.The cooperative operates grain storage elevators in the top U.S. corn producing state, buys and sells grain and owns technology platforms for farmers. “We have taken our systems offline to contain the threat, and we…
Single-factor authentication (SFA) has been added today by the US Cybersecurity and Infrastructure Security Agency (CISA) to a very short list of cybersecurity bad practices it advises against. CISA’s Bad Practices catalog includes practices the federal agency has deemed “exceptionally risky” and not to be used by organizations in the government and the private sector as…
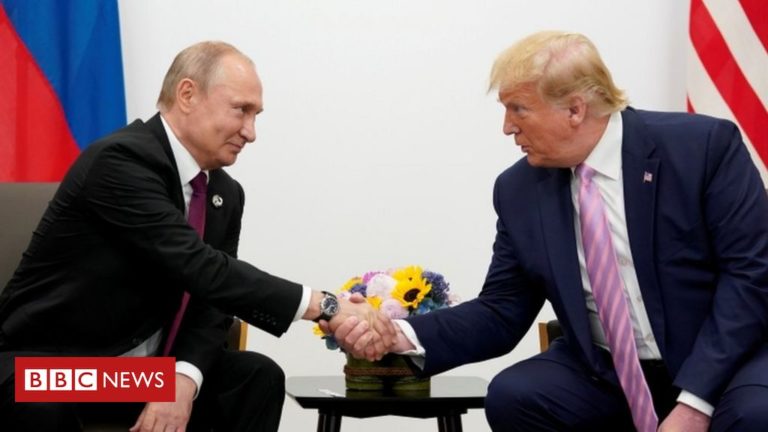
Russian President Vladimir Putin likely authorised attempts to influence last year’s US election in favour of former President Donald Trump, intelligence officials say. Russia has repeatedly denied allegations of election interference. The 15-page report, released on Tuesday by the Office of the….

The website of the Texas Republican Party appeared to be hacked over the weekend and remained largely offline on Monday. TexasGOP.org showed several crude messages on Saturday — the 20th anniversary of the September 11 terrorist attacks — ridiculing the state’s Republican Party and attacking Texas’ new ‘Heartbeat Act.’ Individuals affiliated with the Anonymous movement appear to be the perpetrators….
Insurance company Geico recently filed a data breach notice with the attorney general of California. According to the disclosure, the breach occurred between January 21, 2021 and March 1, 2021 and exposed customers’ driver license numbers. However, Geico did not disclose how many customers might have been affected nor whether the breach was limited to…
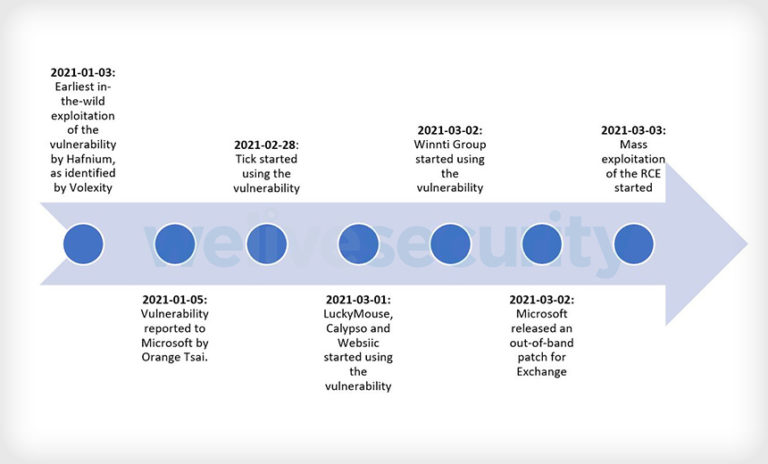
Cybercrime , Forensics , Fraud Management & Cybercrime Some Attacks Predate Microsoft Being Alerted to the Vulnerabilities, ESET Says Doug Olenick (DougOlenick) • March 11, 2021 Microsoft Exchange attack timeline (Source: ESET) Serious vulnerabilities in Microsoft Exchange have been exploited by at least 10 advanced persistent threat groups that have been collectively been…