Crypto Hack Earned Crooks $600 Million
Crypto Hack Earned Crooks $600 Million
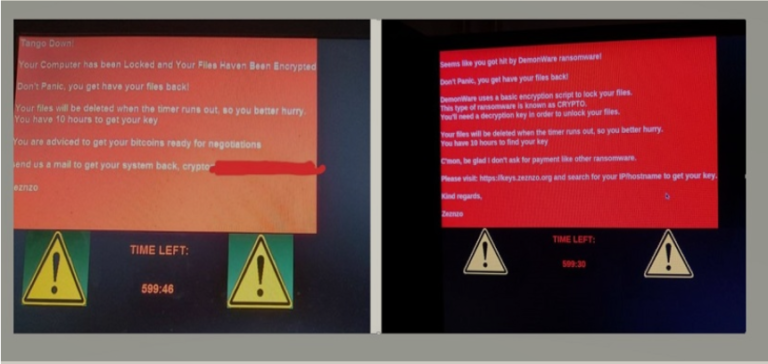
Fraud Management & Cybercrime , Governance & Risk Management , Insider Threat Researchers Learn Details During a Telegram Chat With an Attacker Doug Olenick (DougOlenick) • August 19, 2021 Ransom demand screen provided by the attacker to Abnormal Security A Nigeria-based ransomware gang is conducting a campaign that dangles a $1 million bribe…
Business Continuity Management / Disaster Recovery , Fraud Management & Cybercrime , Fraud Risk Management Hackers Accessed System Containing PII Prajeet Nair (@prajeetspeaks) • July 20, 2021 Campbell Conroy & O’Neil, a Boston-based law firm that serves Fortune 500 firms, including Apple and Pfizer, is continuing its investigation of a ransomware attack in…
The Biden administration has confirmed that ‘state-sponsored Chinese actors’ compromised 13 US pipeline companies as part of a ‘spearphishing and intrusion campaign’ from 2011 to 2013. The coordinated cyber attack targeted 23 pipeline companies in total, according to a report coauthored by the FBI and the Cybersecurity and Infrastructure Security Agency (CISA). Just three of…
Executive Summary This vulnerability is currently undergoing analysis and not all information is available. Please check back soon to view the completed vulnerability summary Informations Name CVE-2021-22337 First vendor Publication 2021-06-03 Vendor Cve Last vendor Modification 2021-06-03 Security-Database Scoring CVSS v3 Cvss vector : N/A Overall CVSS Score NA Base Score NA Environmental Score NA…
Details have emerged about a high severity security vulnerability affecting a software driver used in HP, Xerox, and Samsung printers that has remained undetected since 2005. Tracked as CVE-2021-3438 (CVSS score: 8.8), the issue concerns a buffer overflow in a print driver installer package named “SSPORT.SYS” that can enable remote privilege and arbitrary code execution….
Encryption & Key Management , Governance & Risk Management , Patch Management MTProto Has Since Been Patched Akshaya Asokan (asokan_akshaya) • July 20, 2021 Security researchers identified flaws in messaging app Telegram’s cryptographic protocol, MTProto, that enabled intruders to access encrypted chats and alter the messages. Those flaws have since been patched in…