CVE-2021-35392
CVE-2021-35392
San Francisco: In a big cyber attack, China-based threat actors hacked at least 30,000 organisations across the US, including government and commercial firms, by using Microsoft’s Exchange Server software to enter their networks. The espionage group is known to have exploited four vulnerabilities in Microsoft Exchange Server email software, which provided them access to email…
3rd Party Risk Management , Cyberwarfare / Nation-State Attacks , Fraud Management & Cybercrime Commission Cites National Security Concerns Akshaya Asokan (asokan_akshaya) , Tony Morbin (@tonymorbin) • March 18, 2021 Citing national security concerns, the Federal Communications Commission is moving forward with legal proceedings to ban three Chinese-owned companies from providing telecommunications services…
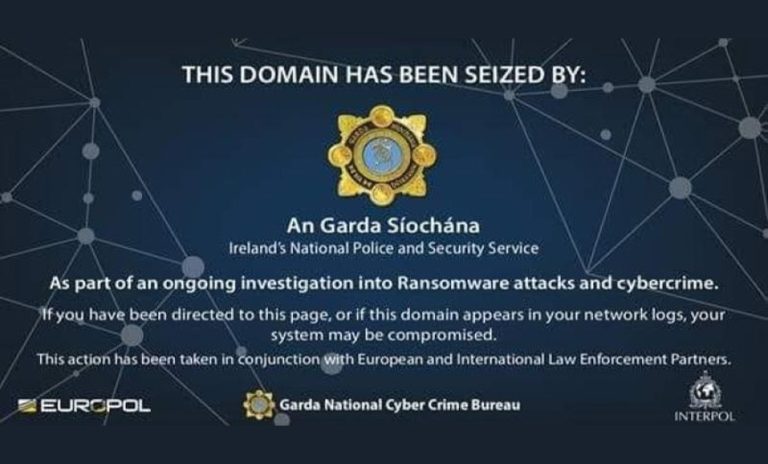
Critical Infrastructure Security , Cybercrime , Cybercrime as-a-service Authorities Target Health Sector Ransom Gang’s IT Infrastructure Mihir Bagwe • September 6, 2021 GNCCB has deployed a “splash screen” on seized domains (Source Garda.ie) The Irish law enforcement body, the Garda National Cyber Crime Bureau, has conducted a “significant disruption operation,” targeting the IT…
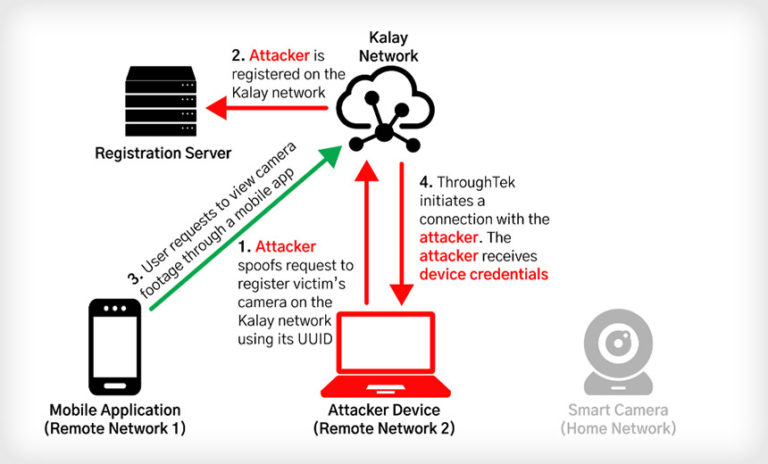
Endpoint Security , Internet of Things Security Researchers: Kalay Protocol Flaw Could Affect Millions of Connected Devices Scott Ferguson (Ferguson_Writes) • August 17, 2021 Example of how an attacker could exploit a vulnerability in ThroughTek’s Kalay protocol (Source: FireEye) FireEye researchers and the U.S. Cybersecurity and Infrastructure Security Agency are warning about a…
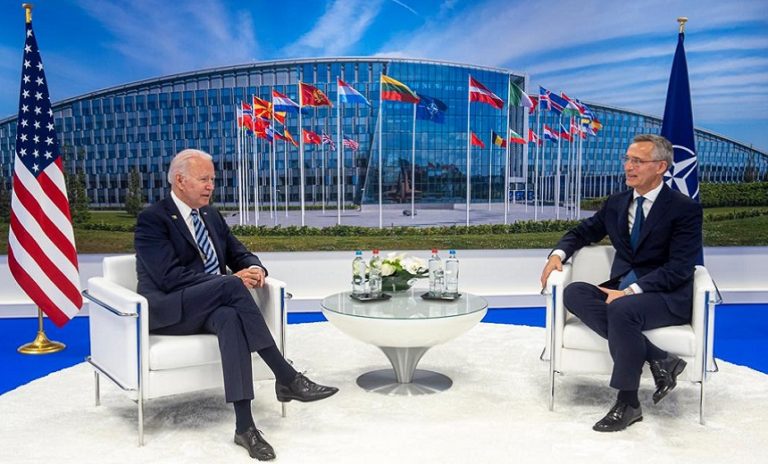
Cyberwarfare / Nation-State Attacks , Fraud Management & Cybercrime , Governance & Risk Management Agreement Comes in Advance of Biden Meeting With Putin on Wednesday Scott Ferguson (Ferguson_Writes) • June 15, 2021 President Joe Biden met with NATO Secretary General Jens Stoltenberg on Monday. (Photo: NATO via Flickr/CC) The U.S. and its NATO…
Microsoft today shared mitigation for a remote code execution vulnerability in Windows that is being exploited in targeted attacks against Office 365 and Office 2019 on Windows 10. The flaw is in MSHTML, the browser rendering engine that is also used by Microsoft Office documents. Ongoing attacks against Office 365 Identified as CVE-2021-40444, the security issue…