Authorities Arrest Another TrickBot Gang Member in South Korea
south korea,trickbot gang member,alleged trickbot developer,time,kbs news,threat,member in south,trickbot’s,authorities arrest,report,arrest another trickbot
Iowa-based farm services provider NEW Cooperative said its systems were offline to contain a cybersecurity incident.The cooperative operates grain storage elevators in the top U.S. corn producing state, buys and sells grain and owns technology platforms for farmers. “We have taken our systems offline to contain the threat, and we…
3rd Party Risk Management , Application Security , Cybercrime DOJ: Russian-Linked Group Breached Office 365 Accounts in 27 Offices Scott Ferguson (Ferguson_Writes) • August 1, 2021 Photo: Salticidae via Flickr/CC The Russian-linked group that targeted SolarWinds using a supply chain attack compromised at least one email account at 27 U.S. Attorneys’ Offices in…
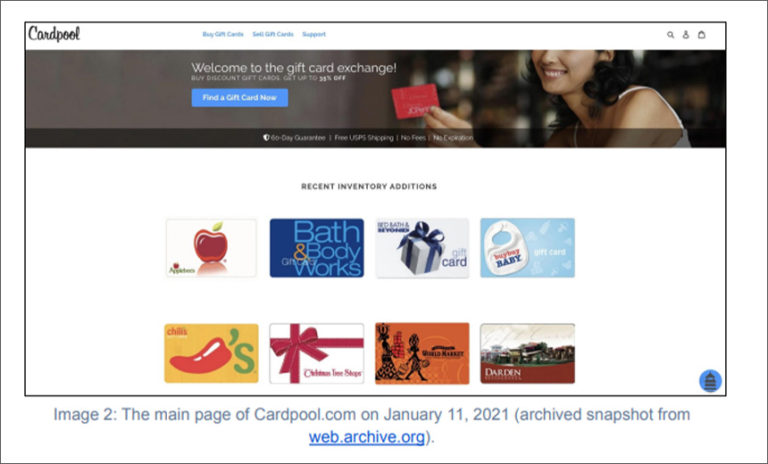
Card Not Present Fraud , Cybercrime , Fraud Management & Cybercrime Gemini Advisory Says Russian Cybercriminal Sold Gift Card, Payment Card Data Akshaya Asokan (asokan_akshaya) • April 6, 2021 The now-defunct Cardpool.com website (Source: Web.Archive.com) A Russian-speaking cybercriminal recently sold on a darknet forum thousands of stolen payment and gift cards that researchers…

Security researchers from Eclypsium have discovered a total of four vulnerabilities in Dell’s SupportAssist software. As the software is pre-installed on the majority of Dell machines running Windows, millions of systems are at risk of remote attack. Eclypsium says that a total of 129 Dell models are affected by the security issues. The chain of…

Linux Kernel Vulnerabilities Can Be Exploited to Bypass Spectre Mitigations | IT Security News 30. March 2021 Recent Linux kernel updates include patches for a couple of vulnerabilities that could allow an attacker to bypass mitigations designed to protect devices against Spectre attacks. read more Like this: Like Loading… Related Tags: SecurityWeek RSS Feed Sponsors…
Business Continuity Management / Disaster Recovery , Fraud Management & Cybercrime , Governance & Risk Management MalwareHunterTeam Finds Updated Capabilities Akshaya Asokan (asokan_akshaya) • March 24, 2021 The REvil ransomware gang has added a new malware capability that enables the attackers to reboot an infected device after encryption, security researchers at MalwareHunterTeam report….